I am
Sedat Özdemir — Ethical Hacker and Cybersecurity Engineer
Sr. Expert Pentest & Vulnerability Management Engineer
Ethical hacker. I think like an attacker and write down what I learn, for everyone.
Sr. Expert Pentest & Vulnerability Management Engineer
Ethical hacker. I think like an attacker and write down what I learn, for everyone.
10+
years in offensive security
Offensive
Defense & process
Curiosity + Discipline =
A closed vuln
Sr. Expert Pentest & Vulnerability Management Engineer
What I'm curious about
How custom models are trained for security work, and how those models are secured themselves.
Areas of expertise
Technical news, fixes and code. Everything comes from my own lab or public sources.
Kill chain, AD, C2 and evasion
7 postsWeb, API, mobile and internal network
7 postsCI/CD, SAST/DAST, containers and K8s
8 postsSample analysis, IOCs and detection rules
7 postsBinaries, drivers and firmware
1 postsLLM security, prompt injection, AI-assisted hunting
3 postsVulnerability news and short takes
3 postsHardware, firmware, SCADA and industrial systems
6 posts Special day
Our Republic turns 103
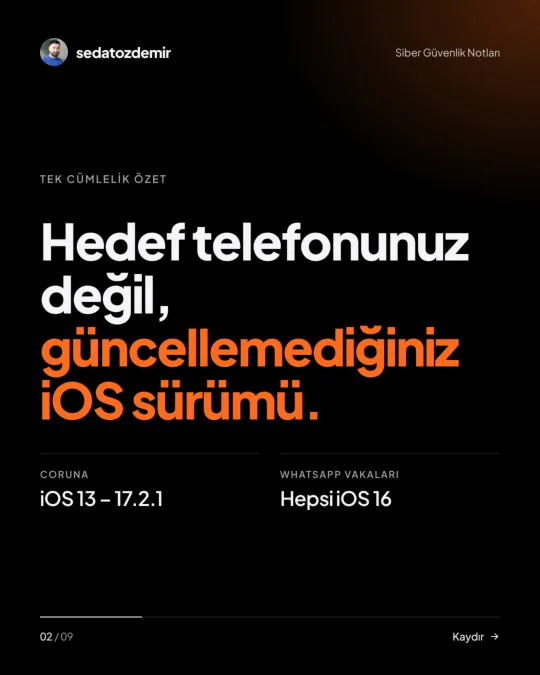
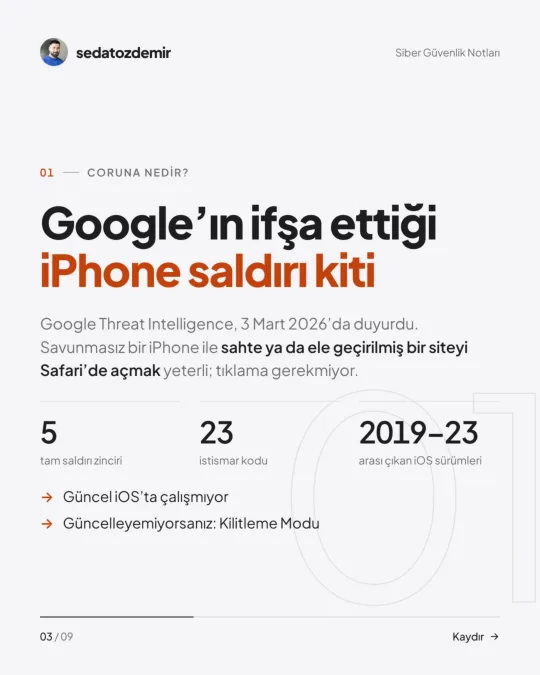
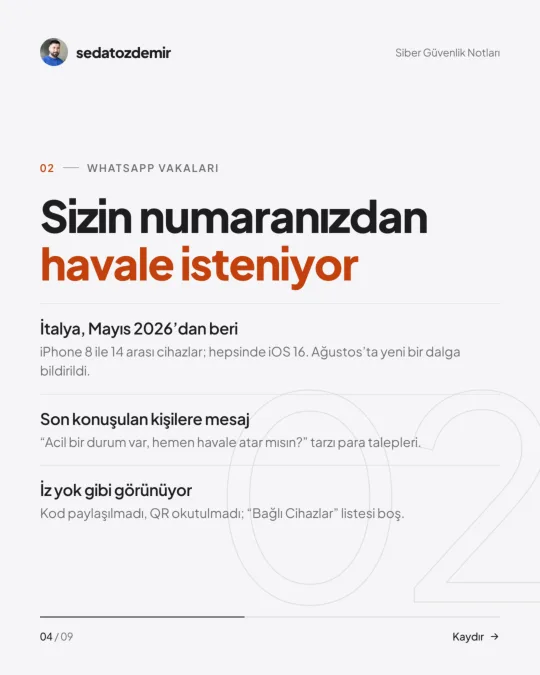
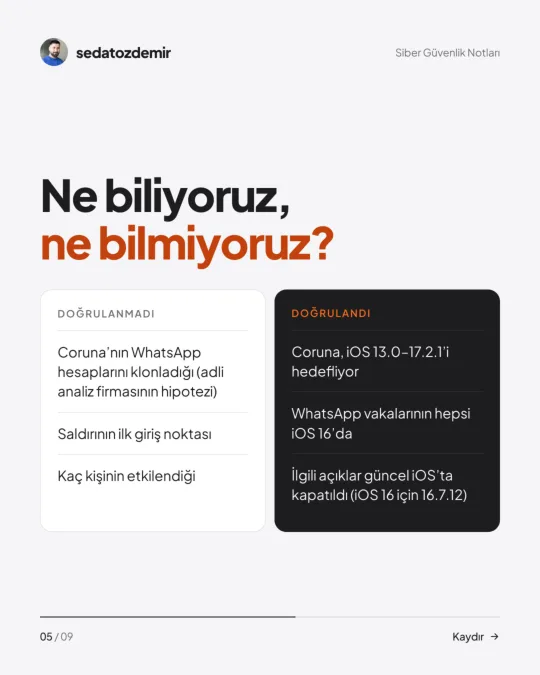
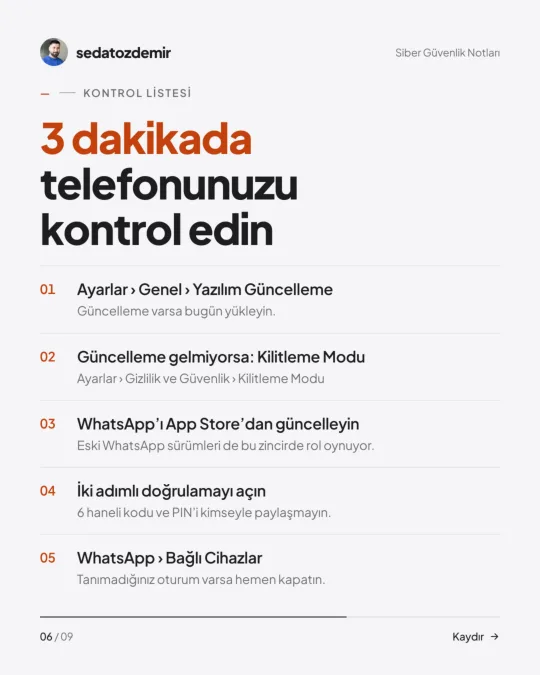
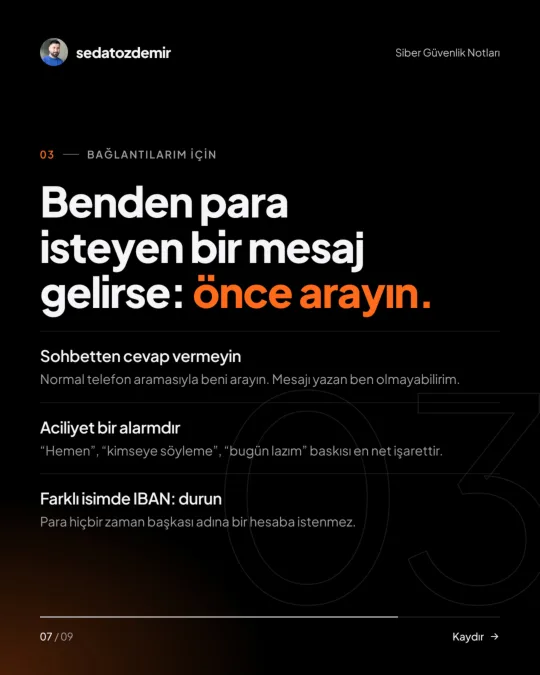
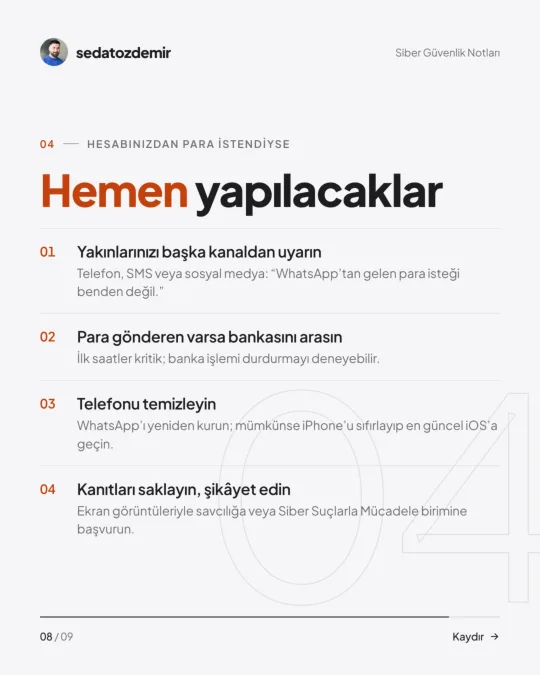
 Carousel · 9 pages01 / 09
WhatsApp: someone is asking for money in your name
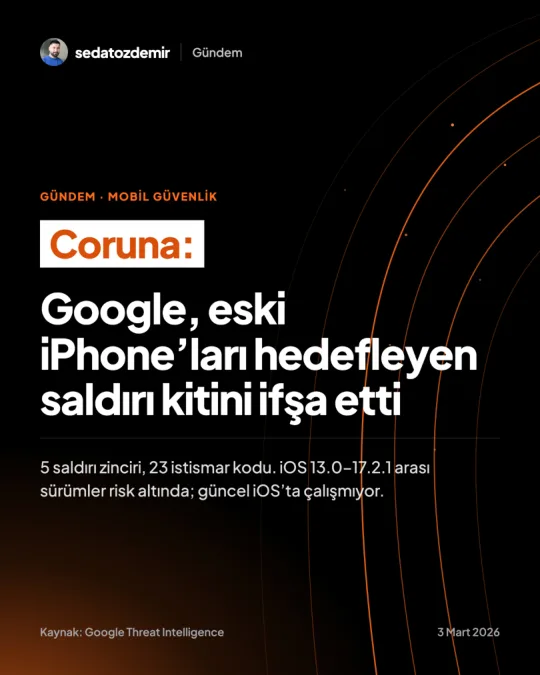 News
Coruna: Google exposes an exploit kit targeting older iPhones
TV, radio, interviews, event talks and news coverage.
Web, API, internal network and mobile penetration testing, red team work, vulnerability management and DevSecOps. I built full stack software in 12 languages, so I understand how an app breaks because I know how it's written. Everything here is my personal opinion and doesn't represent any employer.
Contact
Press requests, conference and meetup invitations, a correction to one of my posts, or just a question. I read every message myself.
If it's an urgent vulnerability report, put "Security" in the subject.